Directly exportable to Jakarta hubs: Explore our certified enterprise security suites, custom integration engines, and ruggedized industrial defense terminals.
Real-time macOS kernel monitoring, cloud threat telemetry streaming, and automated zero-day ransomware isolation designed for corporate Apple environments.
Get Catalog
Bespoke RESTful API & gRPC endpoints engineered to connect localized Jakarta cloud datacenters with distributed legacy enterprise architectures securely.
Get Catalog
Integrated perimeter-to-endpoint protection platform (1-199 nodes) featuring centralized command, deep packet inspection, and hardware firewall sync.
Get Catalog
Comprehensive cross-platform workstation protection featuring localized behavioral engine analysis, device control, and network isolation protocols.
Get Catalog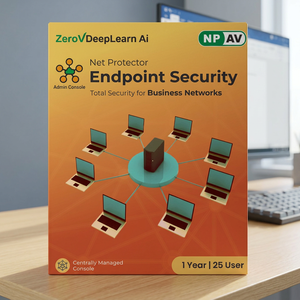
25-User centralized server deployment kit for SME & enterprise branch offices requiring zero-trust network access (ZTNA) and data loss prevention.
Get Catalog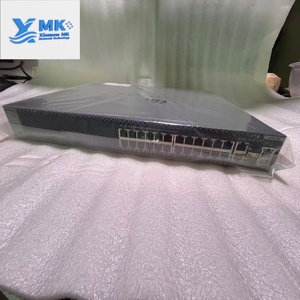
High-throughput hardware security appliance featuring Multi-Vector Virtual Execution (MVX) engines for deep attachment and endpoint payload detonation.
Get Catalog
Intelligent, tamper-proof 370MHz wireless transmission terminal engineered for high-risk industrial facility inspection and secure telemetry logging.
Get Catalog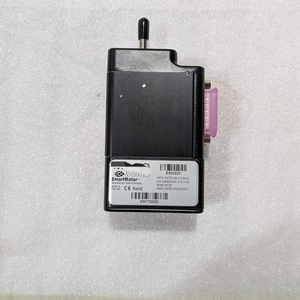
Hardware-enforced endpoint security board delivering secure links, encrypted channel routing, and perimeter defense for mobile industrial fleets.
Get CatalogAs the financial and operational heart of Indonesia, Special Capital Region of Jakarta (DKI Jakarta)—spanning business districts from Sudirman Central Business District (SCBD) to Mega Kuningan and industrial corridors in Cikarang and Karawang—faces an unprecedented wave of sophisticated cyber threats. The fast-paced digitizing economy, accelerated by cloud-native banking platforms, IoT-driven port logistics in Tanjung Priok, and distributed enterprise workforces, presents an expanded attack surface for Advanced Persistent Threats (APTs), state-sponsored ransomware operations, and lateral network intrusions.
As a world-class Endpoint Security Manufacturer & Exporter supplying Jakarta, our engineering organization addresses this dynamic threat landscape directly. Modern endpoint protection can no longer rely on signature-based legacy antivirus mechanisms. True defense-in-depth demands low-footprint kernel telemetry, real-time eBPF behavioral heuristics, automated zero-trust network access (ZTNA), and hardware-enforced micro-segmentation. This whitepaper details our enterprise security hardware, software engines, and local integration capabilities customized to comply with Indonesia's regulatory framework.
Our software agents operating on macOS, Linux, and Windows intercept system calls directly at the kernel tier. By capturing execution context before malware user-space obfuscation takes effect, we ensure near-zero latency mitigation and eliminate performance bottlenecks on enterprise workstations.
Incorporating specialized hardware modules such as the FireEye 4310 and Fev-569gplc PLC controllers, we build cryptographically verified perimeters around legacy operational technology (OT) and critical corporate subnets, preventing lateral malware propagation.
Engineered specifically to satisfy Indonesia's Law No. 27 of 2022 on Personal Data Protection (UU PDP) and BSSN (Badan Siber dan Sandi Negara) security mandates. All data telemetry logging supports local on-premises and Jakarta sovereign cloud data residency storing.
Deploying cybersecurity solutions in Jakarta requires a deep contextual understanding of regional operational realities—ranging from high-density financial districts experiencing strict regulatory oversight to rugged marine industrial ports and distributed manufacturing hubs.
Financial institutions in Jakarta operating multi-branch networks demand granular device compliance checks and immutable auditing. Our Enterprise MAC Stock EDR combined with Qiankun HiSec Firewalls creates an airtight Zero-Trust framework. Telemetry is streamed directly to localized Security Operations Centers (SOCs), isolating compromised endpoint sessions in under 50 milliseconds without disrupting high-frequency trading operations or core banking transaction pathways.
Port operators in North Jakarta rely heavily on handheld inventory terminals and automated crane telemetry systems operating under harsh atmospheric conditions. Utilizing our Handheld Industrial Communication End Point 370M, field operators maintain encrypted, interference-resistant 370MHz radio channel communication. Integrated hardware security chips mitigate physical side-channel tampering and protect container manifest data against unauthorized interception.
In accordance with BSSN Directive No. 4 on Cyber Crisis Management, government databases in Jakarta require strict operational isolation. Our server-managed endpoint suites provide localized air-gapped update capabilities. Administrators can deploy offline threat signature packs, manage role-based access control (RBAC), and enforce cryptographic USB device locks across 10,000+ administrative workstations from a unified on-premise dashboard.
When evaluating endpoint cybersecurity solutions for procurement in Indonesia, hardware performance, kernel compatibility, and protocol adaptability are critical metrics. The following matrix outlines the operational capabilities of our core manufactured security platforms.
| Security Engine Series | Deployment Target | Threat Defense Mechanism | BSSN / UU PDP Readiness | Throughput & Latency Impact |
|---|---|---|---|---|
| Enterprise MAC EDR Subscription | Workstations & Work-from-Home Laptops | eBPF Kernel Telemetry, Behavioral Heuristics, Memory Inspection | Full (Local Log Storage Compatible) | < 0.5% CPU Overhead / < 2ms Latency |
| Qiankun HiSec EDR Edition | Hybrid Branch Offices (1-199 Nodes) | Hardware Firewall Sync, Deep Packet Inspection, Sandboxing | Full (Air-Gapped & Sovereign Cloud Support) | 10 Gbps Wire-Speed Packet Filtering |
| FireEye 4310 Appliance | Enterprise Data Centers & HQ Networks | Multi-Vector Virtual Execution (MVX), Dynamic Attachment Detonation | Full (Encrypted Local Database Storage) | Up to 2.5 Gbps Sandboxing Throughput |
| Handheld Terminal 370M | Field Logistics & Industrial Sites | Hardware Encrypted 370MHz Channel, Tamper-Proof Storage | Full (Hardware-Level Secure Key Storage) | Sub-millisecond Terminal Telemetry Sync |
| Fev-569gplc Security Module | SCADA / PLC / Vehicle Fleets | On-board Micro-segmentation, Encrypted Tunnel Routing | Full (Industrial OT Compliance ISO 27001) | Zero-Packet-Loss Industrial Bus Filtering |
Indonesia's cybersecurity paradigm is undergoing a structural shift driven by legislative reforms and escalating threat sophistication. For enterprise buyers in Jakarta, navigating this landscape requires staying ahead of three major structural developments:
With the full enforcement of Law No. 27 of 2022 (UU PDP), Indonesian organizations failing to secure personal data face penalties up to 2% of annual turnover and criminal liability. Endpoint security is now legally interpreted as a baseline technical measure. Our platforms incorporate built-in Data Loss Prevention (DLP) engines that automatically identify, encrypt, and block unauthorized exfiltration of National Identification Numbers (NIK), financial records, and medical data across all client endpoints.
As manufacturing hubs in Jabodetabek (Jakarta, Bogor, Depok, Tangerang, Bekasi) embrace Industry 4.0, traditional air-gaps between office IT networks and factory-floor SCADA systems are dissolving. Threat actors exploit this convergence to target vulnerable PLC controllers. Our custom industrial hardware solutions (such as the Fev-569gplc) provide protocol-aware inspection (Modbus, DNP3, IEC 60870-5-104) to secure industrial endpoints against destructive malware.
Attackers are actively targeting Indonesian organizations with localized Bahasa Indonesia AI-generated spear-phishing campaigns designed to bypass standard email filters. Our FireEye 4310 dynamic execution engine explodes embedded links and attachments in isolated virtual environments prior to delivery, detecting zero-day weaponized office documents before end-users interact with them.
Sourcing endpoint security equipment and software subscriptions through indirect distributor chains often introduces inflated costs, delayed patch cycles, and restrictive licensing regimes. Partnering directly with an established Manufacturer & Exporter delivers clear operational and economic advantages to Jakarta-based enterprises and regional system integrators.
We provide low-level API source access and bespoke firmware modifications. Whether you require customized REST microservices, specialized telemetry streaming to proprietary SIEM platforms (Splunk, Elastic, Sentinel), or tailored UI localization in Bahasa Indonesia, our engineering team delivers directly to your spec.
Our dedicated international trade department handles all export documentation, Certificate of Origin (COO), and customs formatting required for expedited clearing at Soekarno-Hatta International Airport air-cargo hubs and Tanjung Priok sea freight terminals, eliminating import friction.
We offer scalable licensing tiers ranging from 25-user SME bundles (Net Protector Endpoint Business) up to multi-thousand endpoint enterprise enterprise subscriptions—free from arbitrary annual price hikes or hidden seat renewal penalties.
Our senior cybersecurity architects work alongside enterprise procurement teams, MSSPs, and government contractors to specify, prototype, and export tailor-made endpoint protection solutions.
Addressing common technical, legal, and logistical questions regarding the import and deployment of our endpoint security solutions in Indonesia.
A: Our endpoint platforms feature localized data classification and loss prevention engines that monitor data-in-use, data-in-motion, and data-at-rest. Telemetry generated by the software agents can be anchored directly to local Jakarta data centers (such as AWS Jakarta Region, Google Cloud Jakarta, or private on-premise infrastructure), fulfilling strict sovereign data handling mandates mandated by Kominfo and BSSN.
A: Air freight shipments delivered directly to Soekarno-Hatta (CGK) typically arrive within 3 to 5 business days following order confirmation and export clearing. Bulk sea cargo targeting Tanjung Priok port (JKT) has a typical transit lead time of 10 to 14 days, complete with standardized commercial invoices, packing lists, and Certificate of Origin (COO) document sets.
A: Yes. For sensitive military, government, or critical infrastructure networks in Jakarta requiring complete isolation from the public internet, we provide local threat intelligence distribution servers. Threat signature updates, machine learning model weights, and agent policies are deployed internally via local mirror repositories without sending telemetry outside your physical network boundary.
A: Absolutely. As an original OEM/ODM manufacturer, we provide white-label branding options, custom API endpoints microservice connectors, bespoke installer packaging, and deep integration hooks into regional Security Operations Center (SOC) platforms.
A: Our software agents are built using highly optimized C/C++ and Rust kernel drivers, consuming less than 1% CPU utilization during normal operations and requiring under 120MB of RAM memory overhead, ensuring seamless performance across older legacy PCs as well as high-performance macOS workstations.
A: You can click the "Get Catalog" buttons on this portal to connect directly with our international sales and engineering team. We provide trial software license keys, detailed technical datasheets, and direct architectural consultations within 24 business hours.
Empower your organization with manufacturer-direct pricing, advanced threat detection engines, and customized cyber infrastructure designed for Jakarta’s complex business environment.

