Precision-engineered protective covers, heat-resistant suits, custom equipment shields, and zero-trust perimeter defense solutions exported worldwide.
Modern enterprise perimeters have fundamentally evolved beyond rigid network borders. In an interconnected multi-cloud environment, mission-critical application infrastructures face unprecedented threats—ranging from sophisticated Layer 7 Distributed Denial of Service (L7 DDoS) attacks and credential stuffing to advanced zero-day exploits targeting the OWASP Top 10 vulnerabilities. Establishing an uncompromising cybersecurity stance requires partnering with a trusted Cloud WAF supplier & exporter capable of combining real-time threat intelligence with ultra-low latency scrubbing networks.
A cloud-native Web Application Firewall (WAF) operates as a dynamic, reverse-proxy security barrier deployed at the edge of global Anycast networks. By inspecting HTTP/HTTPS traffic prior to origin server ingestion, our next-generation Cloud WAF engine evaluates payload integrity, SSL/TLS handshake metadata, query parameter structures, and HTTP headers using a synthesis of signature-based rules and dynamic behavioral analysis algorithms.
Real-time blocking of SQL Injection (SQLi), Cross-Site Scripting (XSS), Remote Code Execution (RCE), and Broken Access Control vectors.
Multi-terabit Anycast mitigation scrubbers designed to absorb massive HTTP floods, Slowloris attacks, and HTTP/2 Rapid Reset exploits effortlessly.
Advanced browser fingerprinting, TLS finger-printing (JA3/JA4), and challenge-response mechanisms that thwart malicious web scrapers and credential-stuffing bots.
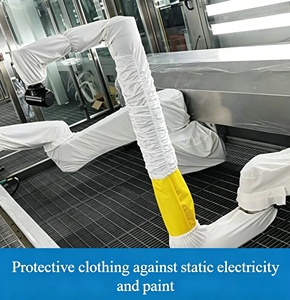
Furthermore, cloud application defense demands seamless synergy between virtual digital firewalls and physical operational technology (OT) equipment safeguards. Industrial automation hubs hosting enterprise web management portals rely on robust physical enclosures—such as heavy-duty neoprene gear shields, flame-retardant robotic jackets, and anti-static protective suits—to protect critical edge processing hardware against harsh physical contaminants while Cloud WAF protocols safeguard the network layer.
Selecting the optimal enterprise security paradigm requires analyzing architectural tradeoffs between cloud SaaS, reverse proxy edge nodes, and hardware-integrated perimeter systems.
| Evaluation Parameter | Cloud Anycast SaaS WAF | Legacy On-Prem Appliance | Edge Mesh (eBPF / Wasm) |
|---|---|---|---|
| Global Mitigation Capacity | 15+ Tbps Distributed Anycast | Limited by Hardware Link (10-40 Gbps) | Scalable Multi-Region PoPs |
| Deployment Timeframe | < 15 Minutes (DNS / CNAME Switch) | Weeks (Hardware Provisioning) | Instant Container Injection |
| Zero-Day Protection SLA | Automated Global Rule Push (< 5 mins) | Manual Patch & Firmware Update | ML Signatureless Heuristics |
| API & OpenAPI Support | Native JSON / REST / gRPC Validation | Basic Signature Matching | Strict Schema Enforcement |
| Physical & OT Integration | Hybrid API Bridge to Industrial Edge | Local Rack Mounting Only | Micro-gateway Edge Modules |
As enterprise digital transformation accelerates globally, enterprise procurement officers and Chief Information Security Officers (CISOs) face shifting regulatory and operational benchmarks. The convergence of cloud application security, API risk mitigation, and industrial robotic automation has created new procurement mandates for dual-layer physical and digital defense systems.
Organizations are rapidly migrating away from standalone perimeter security tools toward unified Secure Access Service Edge (SASE) platforms. Modern Cloud WAF solutions are no longer evaluated solely on basic packet-filtering capabilities; buyers now demand integrated Content Security Policy (CSP) enforcement, Zero-Trust micro-segmentation, and dynamic Rate Limiting software built into the scrubbing network.
With regulations such as PCI-DSS 4.0, ISO/IEC 27001:2022, GDPR, and HIPAA enforcing rigorous log retention and data privacy rules, multinational organizations require Cloud WAF suppliers that offer regional log sovereignty and localized TLS termination nodes. Trusted exporters must provide granular compliance documentation, audit-ready reporting portals, and verifiable encryption standards across all points of presence (PoPs).
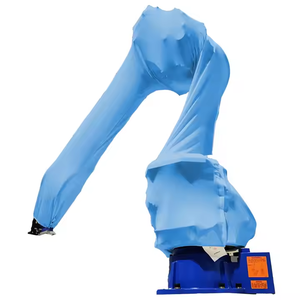
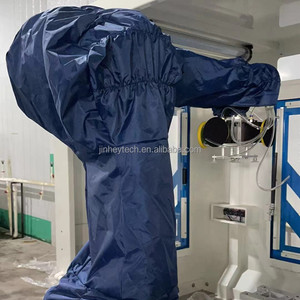
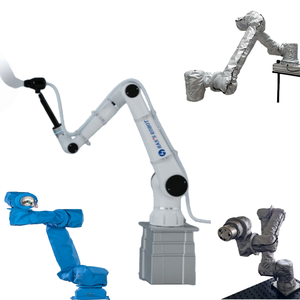
In automated manufacturing environments, web-managed cobots and robotic arms (including Kuka, ABB, Kawasaki, Universal Robots, JAKA, and Kinova) serve as the physical interface for cloud commands. Procuring heavy-duty, flame-retardant, anti-static, dust-proof, and water-resistant protective jackets ensures continuous hardware uptime. Combining physical gear box shields with digital WAF security prevents both physical mechanical failures and unauthorized remote control exploits.
Replacing static threshold rules with machine learning models that detect novel attack patterns and low-and-slow DDoS attempts in real time.
Automatic endpoint cataloging, drift detection, and blocking of rogue/shadow APIs across GraphQL and RESTful enterprise backends.
Factory-tested custom skeleton designs, heat insulation covers, and precision fitment tailored to international OEM specifications.
To establish true competitive advantage in web infrastructure protection, modern security architectures must analyze dynamic attack topologies across the HTTP protocol stack. Below is an exhaustive breakdown of how an enterprise-grade Cloud WAF mitigates modern cyber threats while preserving rapid application response rates.
Automated threats account for over 40% of all global web traffic. Scripted botnets utilize headless Chrome, Puppeteer, and Playwright instances to bypass rudimentary user-agent filters. Our cloud security framework deploys non-intrusive client-side JS challenges combined with TLS Fingerprinting (JA3/JA4 algorithm hashing). By analyzing TCP window sizes, cipher suite ordering, HTTP/2 SETTINGS frames, and canvas rendering behavior, the engine calculates a real-time risk score for incoming sessions.
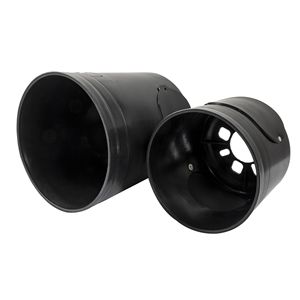
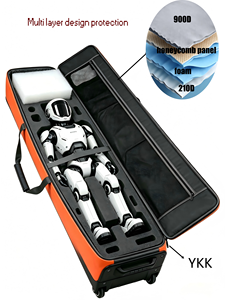
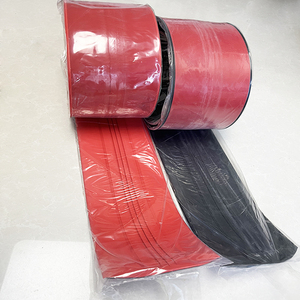
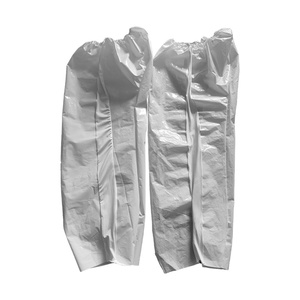
Expanding enterprise defense beyond software layers, our physical protection division manufactures high-durability industrial covers. Designed for heavy machinery, agricultural equipment gearboxes, and multi-axis industrial cobots, these custom covers utilize heavy-duty neoprene, anti-static fiberglass, and flame-retardant composite fabrics. Each protective suit is crafted to resist abrasive sand, rock impacts, oil penetration, and elevated thermal exposure in demanding factory and field conditions.
Leveraging decades of specialized manufacturing craftsmanship, modern ISO certified quality control standards, and global logistics networks, our organization delivers complete protection ecosystems for enterprise clients globally.
Dedicated technical support team delivering response times under 1 business day for custom quotes, specifications, and sample dispatch.
Precision 3D CAD modeling, custom skeleton design, laser branding, and bespoke tailor-fitting for all major robotic and industrial equipment brands.
Robust international supply chain exporting to over 20+ countries with complete regulatory documentation, custom clearance support, and fast lead times.
Direct technical and operational answers to support your enterprise sourcing, procurement, and integration workflows.
Our globally distributed Anycast network routes user traffic to the nearest scrubbing node. Advanced edge caching and HTTP/3 optimization ensure sub-2ms processing latency, frequently improving site load speed compared to un-proxied origin architectures.
Yes. We engineer factory-customized, flame-retardant, anti-static, and waterproof protective suits for major industrial cobot arms including Kuka, ABB, Kawasaki, Universal Robots, JAKA, HANS, HUAYAN, and Kinova based on exact CAD specs.
Our Cloud WAF utilizes dynamic AI heuristic scoring instead of simple binary blocking. Traffic exhibiting suspicious patterns is subjected to non-intrusive background JavaScript verification before any request blocking occurs.
For both physical industrial protective equipment catalog lines and cloud security licensing, our team provides flexible bulk pricing schedules. Custom prototypes and sample evaluations are confirmed within 1 business day.
Absolutly. The engine automatically indexes incoming REST, SOAP, JSON, and GraphQL endpoints, enforcing strict schema compliance and blocking payload tampering or unlisted shadow API requests.
Yes, we produce dedicated dust- and water-resistant food-grade robot arm protective jackets certified for hygienic environments, pharmaceutical manufacturing, and washdown zones.
The DNS/CNAME Anycast architecture operates independently of underlying infrastructure hosters. It seamlessly shields endpoints hosted across AWS, Google Cloud, Azure, on-premises private datacenters, or edge servers.
Click the "Get Catalog" button anywhere on our portal to connect instantly with our global sales engineering team for personalized catalog access, architectural consultation, and custom RFQ submission.
Connect with our senior technical procurement team today to request complete product catalogs, custom CAD sample fitment, or architectural Cloud WAF consultations.
Get Catalog
