Explore our high-performance hardware modules, edge shields, and automated threat verification units designed for zero-latency device identification and bot mitigation.
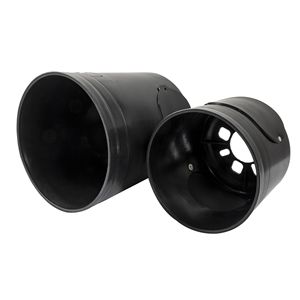
Industrial-grade device entropy collector and hardware shield for rugged edge servers, protecting critical IoT gateways from device spoofing.
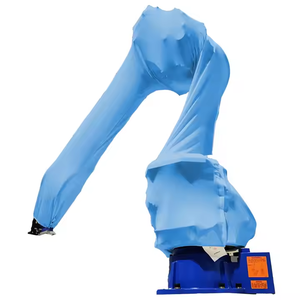
Custom skeleton design hardware housing engineered to shield physical identity sensors and network telemetry collectors in high-risk zones.
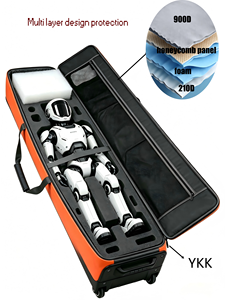
Portable field testing unit and security appliance designed for on-site browser fingerprinting calibration and signal validation.
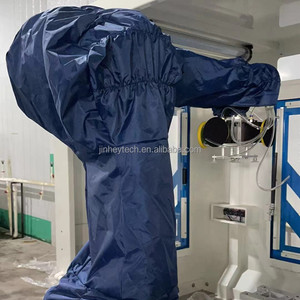
High-heat resistant physical security chassis for critical TLS fingerprint parsing units compatible with enterprise server racks.
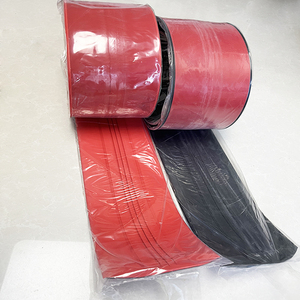
Reinforced defense module mitigating physical signal interference and high-frequency friction on edge computing nodes.
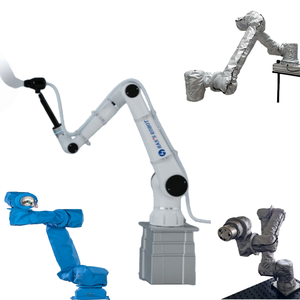
Flexible physical housing for multi-axis cobot controllers and automated browser telemetry verification hardware units.
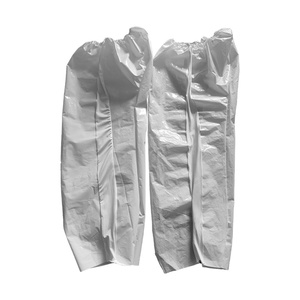
Hygienic, IP67-rated hardware casing for food-grade cleanrooms and high-precision biometric entropy devices.
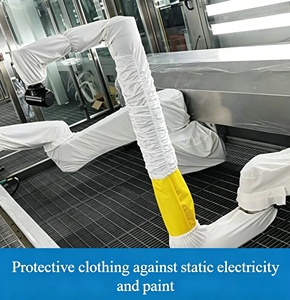
All-weather oilproof, heat-resistant protective sleeve for high-density edge network appliances and anti-bot verification nodes.
Modern cybersecurity and identity verification architectures have shifted dramatically from IP-based rate limiting and cookie tracking to high-entropy browser fingerprinting. As web privacy protocols (such as Apple Safari’s ITP, Google Chrome’s Privacy Sandbox, and Firefox’s ETP) restrict traditional cookies, global enterprises rely on browser fingerprinting manufacturers and software engine suppliers to maintain operational security, prevent credential stuffing, and eliminate automated bot attacks.
Browser fingerprinting operates by evaluating hundreds of client-side signals emitted during a standard HTTPS session. These signals form a unique identifier (hash) based on the specific hardware, operating system, graphics rendering engine, and browser stack configuration of the connecting client. Understanding the procurement landscape of top manufacturers and tech suppliers is paramount for CTOs, CISOs, and enterprise IT buyers seeking non-intrusive threat mitigation without sacrificing user conversion.
Harvests microscopic rendering discrepancies across GPU hardware drivers and anti-aliasing algorithms to build unique device hashes.
Measures audio processing signals and frequency response curves generated by underlying audio hardware and system drivers.
Analyzes packet handshakes, cipher suites, SSL/TLS extensions, and TCP stack configurations at the edge network gateway level.
A technical assessment of leading global manufacturers, SDK developers, and specialized security hardware vendors delivering device entropy intelligence.
Provides high-accuracy visitor identification using hybrid client-side signals and server-side machine learning. Achieves 99.5% identifier stability across browser updates and incognito modes.
Specializes in rugged hardware enclosures, edge sensors, and custom OEM physical security modules designed to host device entropy SDKs and protect anti-bot edge gateway hardware.
Integrates deep telemetry at the edge server level. Combines network layer JA4 fingerprints with browser JavaScript execution patterns to neutralize massive DDoS and web scraping attacks.
Leverages modern signal verification to validate real human interaction. Analyzes client-side API modifications, headless browser anomalies, and browser fingerprint manipulation.
Deploys passive browser fingerprinting natively across global edge locations. Utilizes machine learning heuristic scores to block headless browsers and automated scripts instantly.
Focuses on financial industry fraud detection, linking browser hardware fingerprints with global digital identity intelligence networks to stop account takeover (ATO).
Processes millions of device signatures per second. Uses in-memory processing to compare browser canvas entropy and device orientation events against known threat profiles.
Protects complex web applications by correlating client-side browser fingerprint inconsistencies with backend server anomalies to identify sophisticated API abuse.
Delivers rapid JavaScript device fingerprinting for e-commerce brands and fintech platforms. Extracts screen resolution, WebGL vendor strings, and installed extensions.
Monitors user session risk by identifying device hardware changes, browser fingerprint shifts, and proxy/VPN routing anomalies in real time.
Compare key architectural capabilities across enterprise browser fingerprinting categories before finalizing procurement decisions:
| Evaluation Parameter | Client-Side JS SDK | Edge Security Gateway | Custom OEM Hardware Module |
|---|---|---|---|
| Primary Entropy Source | Canvas, WebGL, Fonts, AudioContext | JA3/JA4 TLS, TCP/IP Stack, IP Reputation | Physical Sensor Telemetry & Hardware IDs |
| Average Processing Latency | 1.5ms – 5ms | < 1ms (Edge Server) | Zero Latency (Dedicated Processing) |
| Privacy Compliance (GDPR/CCPA) | Requires Hash Anonymization | Fully Compliant (No PII Stored) | Hardware Isolated (Maximum Privacy) |
| Resistence to Anti-Detect Browsers | Medium to High (Machine Learning) | High (Network Layer Signals) | Ultra High (Physical Hardware Verification) |
| Primary Industry Use Case | Fintech, E-Commerce, SaaS Portals | High-Traffic CDNs, Cloud Platforms | Industrial IoT, Defense, Edge Server Protection |
As enterprise cyber threats escalate, B2B procurement officers and IT security managers must align sourcing strategies with emerging technological paradigms. Below are key trends defining the next generation of browser fingerprinting solutions:
Browser fingerprinting technology has evolved through distinct technological waves, moving from intrusive client probing to seamless, invisible entropy analysis.
Relied heavily on user-agent strings, HTTP headers, and local storage cookies. Vulnerable to simple user clearing, VPNs, and header spoofing.
Introduced active script probing: drawing hidden WebGL shapes, measuring font rendering variations, and interrogating web API objects.
Combines obfuscated WebAssembly (WASM) collectors with passive behavioral analytics (mouse movement micro-jitter, keystroke dynamics) and edge network signatures.
Combining decades of precision engineering with modern ISO 9001 certified quality controls, we supply physical security enclosures, custom edge nodes, and hardware solutions tailored for global cyber defense suppliers.
We control raw materials, chassis geometry, surface finishing, and quality assurance in our owned facility, guaranteeing batch consistency and rugged reliability for edge server deployments.
From custom IP67 waterproof enclosures for cleanroom fingerprint sensors to laser-etched branding and private label packaging, our team responds to customized requests within 1 business day.
Every physical product SKU undergoes rigorous thermal, anti-static, flame-retardant, and structural stress testing to withstand industrial computing environments.
With complete export-ready documentation and multi-category SKU coverage (over 469 active product lines), we ensure seamless logistics to distributors and technology system integrators worldwide.
Addressing essential technical, operational, and commercial questions asked by enterprise procurement managers.
Browser fingerprinting is a method of identifying individual web browsers and hardware devices by collecting client-side configuration parameters—such as canvas rendering anomalies, installed fonts, screen specs, and WebGL graphics drivers. Unlike IP addresses, which change dynamically across VPNs and mobile networks, a browser fingerprint remains consistent regardless of network changes or cookie clearing.
Yes, provided the solution is designed with privacy-first principles. Leading enterprise fingerprinting suppliers process raw client signals into one-way cryptographic hashes (salt + SHA-256) without collecting personally identifiable information (PII). When used strictly for fraud prevention, security, and bot mitigation, it complies with legitimate interest clauses under GDPR and CCPA guidelines.
Advanced fingerprinting engines analyze deep signal consistency. When an anti-detect browser attempts to spoof parameters (e.g., faking a Mac OS User-Agent on a Windows machine), micro-discrepancies between the audio API, CPU core counts, WebGL vendor strings, and TLS handshakes trigger an inconsistency alert, exposing the fake profile immediately.
Modern enterprise SDKs utilize asynchronous WebAssembly (WASM) scripts optimized for minimal CPU execution time. Signal extraction typically takes less than 2.5 milliseconds and runs entirely in the background without blocking page DOM rendering, ensuring zero impact on end-user experience or Core Web Vitals.
Yes. As a primary precision equipment manufacturer, we supply custom-engineered protective housings, anti-static server shields, and waterproof edge sensor covers tailored to your exact physical specifications, complete with custom laser branding and OEM packaging.
Minimum order quantities depend on the specific product line and custom specifications required. Our engineering team confirms pricing, MOQ, and sample delivery schedules within 24 hours of receiving your detailed technical brief.
JA3/JA4 fingerprinting analyzes the SSL/TLS client hello handshake at the network gateway level. Combining network-level TLS signatures with client-side JavaScript hardware entropy creates a two-factor verification matrix that blocks sophisticated headless bots before they can consume expensive backend API resources.
We provide full sample development and testing protocols. Enterprise buyers can evaluate physical prototypes, structural resilience, material specifications, and logo laser-etching quality before authorizing full-scale production runs.
Consult with our engineering and procurement team today. Receive tailored specification recommendations, competitive factory-direct pricing, and custom OEM manufacturing lead times within 24 hours.

