Explore our ISO 9001:2015 certified hardware appliances, security software bundles, microservices API architectures, and industrial transmission endpoints engineered for global enterprise procurement.
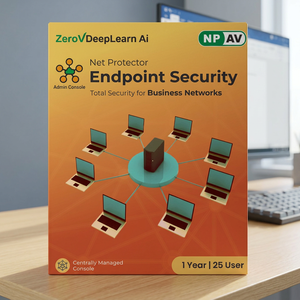
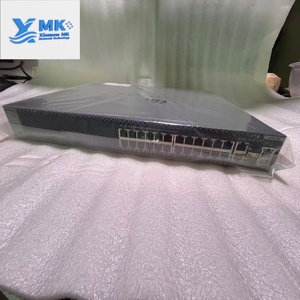
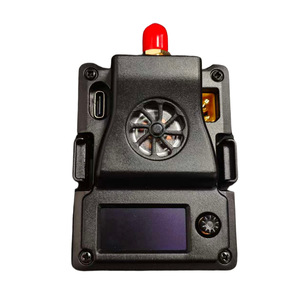
The global threat landscape has fundamentally shifted the nature of network perimeters. In an era dominated by distributed workforces, hybrid cloud workloads, zero-day telemetry exploits, and industrial Operational Technology (OT) convergence, the physical and logical endpoint represents the ultimate battlefield for cybersecurity resilience. For global IT distributors, Managed Security Service Providers (MSSPs), telecom carriers, and enterprise brand owners, sourcing endpoint protection solutions directly from specialized Original Equipment Manufacturers (OEM) and Original Design Manufacturers (ODM) offers unprecedented advantages in cost optimization, firmware customization, supply chain transparency, and hardware-level trust initialization.
As a specialized engineering ecosystem and exporting powerhouse, our manufacturing facilities integrate precision hardware assembly, board-level Surface Mount Technology (SMT), embedded firmware flashing, Hardware Security Module (HSM) provisioning, and white-label software UI customization under a rigorous ISO 9001:2015 quality management system. From rackmount network threat protection appliances to ruggedized industrial inspection terminals and cross-platform Endpoint Detection and Response (EDR) software agent packaging, we provide end-to-end original manufacturing pipelines tailored to your market specifications.
We combine decades of hardware engineering craft with agile software integration systems to deliver market-ready endpoint security products.
Our ODM hardware lines feature onboard cryptographic coprocessors, secure bootloaders, and zero-trust silicon anchors certified to FIPS 140-3 and Common Criteria standards, preventing physical tampering and unauthorized firmware flashing.
From custom chassis laser etching, silk-screened metal enclosures, and bespoke retail packaging to white-labeled agent installers, branded administrative portals, and custom API documentation, your brand retains complete customer mindshare.
Shipping to over 20 global export markets with comprehensive CE, FCC, RoHS, REACH, and export-control encryption permits. Fast technical response within 1 business day for custom quotes, sample validation, and RFP response.
Strategic analysis for procurement officers, enterprise CISOs, and hardware importers looking to maintain competitive advantage over a 5-year technology horizon.
Procurement mandates are moving beyond pure software agent subscriptions. Future enterprise tenders require endpoints to feature hardware-enforced device identity via immutable cryptographic keys burnt directly into board silicon at the factory stage. Sourcing from factories capable of micro-code provisioning guarantees protection against bootkits and baseboard manipulation.
Next-generation EDR and XDR requirements demand real-time behavior analysis directly on the endpoint without creating cloud latency or bandwidth saturation. OEM factories are responding by integrating dedicated Neural Processing Units (NPUs) and high-efficiency ARM/RISC-V coprocessors into handheld terminals and industrial security gateways.
The boundary between commercial enterprise IT and critical infrastructure OT is dissolving. Importers are increasing purchasing allocations for industrial-grade endpoints—featuring IP67/IP68 ingress protection, wide temperature resistance (-40°C to +85°C), and native support for PLC, HART, and wireless industrial protocols.
Monolithic security suites are being replaced by modular microservices. B2B buyers favor security software platforms that expose comprehensive RESTful and gRPC APIs, allowing white-label integrators to embed specialized monitoring plugins, SIEM connectors, and automated remediation workflows dynamically.
Modern malware attacks operate across heterogeneous enterprise environments spanning macOS, Linux kernels, Windows enterprise builds, and customized Android handheld inspection units. Original Design Manufacturers must engineer agent codebases that operate efficiently at kernel level without triggering system instability. By employing eBPF (Extended Berkeley Packet Filter) technology in Linux ecosystems and System Extensions in macOS, modern OEM EDR software achieves deep packet monitoring, process isolation, and automated ransomware rollback with sub-1% CPU overhead.
Isolated security point products create dangerous monitoring blind spots. Modern OEM threat protection appliances (such as the FireEye 4310 architecture class and HiSec firewall integrations) bridge the gap between network-level deep packet inspection (DPI), email MTA sandboxing, and endpoint execution logs. Ingesting high-velocity telemetry across network taps and host agents enables automated threat graph correlation and immediate honeypot isolation.
For specialized industrial communication endpoints (e.g., 370M inspection terminals and PLC-enabled security nodes), secure wireless transmission protocols are paramount. Factory customizations incorporate AES-256 encrypted radio links, hardware-accelerated VPN tunnels (WireGuard/IPsec), dual-SIM failover mechanisms, and safe-link verification modules directly into portable hardware form factors, ensuring data integrity across hazardous industrial environments.
Use this standardized matrix to specify your technical criteria when requesting engineering samples or formal quotation proposals from our export department.
| Deployment Category | Hardware / System Architecture | Supported OS / Environments | Key OEM Customization Parameters | Target B2B Application |
|---|---|---|---|---|
| Enterprise EDR Agents | X86_64 / ARM64 lightweight client runtime | macOS, Windows Server, Linux (RHEL/Ubuntu) | White-label UI, custom server IP telemetry streams, installer branding | Corporate IT networks, MSSP managed endpoints |
| Threat Appliances | Rackmount 1U/2U server, multi-GbE SFP+ ports | Hardened Linux appliance OS, inline firewall engine | Chassis front bezel design, custom BIOS splash, deep API integration | Datacenter perimeter, enterprise network core |
| Industrial Terminals | Ruggedized handheld, 370M screen, shockproof body | Custom embedded Android / RTOS | Custom frequency bands, laser scanner module, customized inspection apps | Oil & Gas, smart logistics, power grid inspection |
| API Microservices | Docker/Kubernetes microservice containers | Cloud-native, AWS / Azure / On-Prem Private Cloud | Custom endpoint router, token authentication schema, custom SDKs | FinTech, IoT device management platforms |
| On-board PLC Modules | Embedded industrial board, DIN-rail mounting | Real-time firmware, industrial bus protocols | Safe-link filtering algorithms, customized I/O pin layouts, custom enclosure | Automotive manufacturing, smart factory automation |
Direct answers regarding production lead times, minimum order quantities (MOQ), intellectual property, and technical support SLAs.
For standard software agent subscriptions and API microservices licensing, MOQ starts at 100-250 seats/nodes. For physical hardware appliances and custom PCB board assembly, standard OEM branding starts at 100 units, while complete ODM custom mold tooling and chassis manufacturing typically requires 500-1,000 units depending on enclosure complexity.
We execute legally binding non-disclosure agreements (NDAs) prior to any engineering disclosures. Source code, private API keys, and custom cryptographic firmware are segregated within air-gapped engineering environments. Customers retain 100% ownership of bespoke software modules and proprietary design assets developed under contract.
Every hardware production batch undergoes automated optical inspection (AOI), high-voltage burn-in testing (48+ hours), physical drop testing, and automated functional firmware validation under our ISO 9001:2015 process framework. Software builds are subjected to static/dynamic vulnerability scanning and compatibility regression suites.
Yes. We provide complete white-label transformation. This includes customizing code signatures, installer binary icons, EULA agreements, splash screens, dark/light admin dashboards, error notification emails, and domain name endpoints so your end clients interact exclusively with your brand identity.
Standard white-label software evaluation builds and digital API sandboxes can be provisioned within 1 to 3 business days. Physical hardware prototype samples with laser-etched branding and customized firmware preloads typically ship within 7 to 14 business days via expedited international freight.
Our hardware product lines comply with major global regulatory frameworks, carrying CE, FCC Class A/B, RoHS 2.0, REACH, and WEEE certifications. Specialized industrial inspection units also feature ATEX explosion-proof certifications for hazardous environment operations.
We provide long-term maintenance agreements (1 to 5 years) covering quarterly vulnerability patches, virus definition database stream updates, OS compatibility updates (e.g., major macOS/Windows releases), and 24/7 Tier-3 engineering escalation support for enterprise-level distributors.
You can click any of the "Get Catalog" buttons on this portal to connect directly with our engineering sales team via live consultation, or send your technical specification brief directly to our export office. We guarantee detailed quotation proposals and MOQ confirmations within one business day.
Partner with an established exporter and engineering team. Get full access to technical datasheets, wholesale pricing schedules, and custom white-label sample kits.

