Turnkey OEM/ODM hardware manufacturing engineered for Zero-Trust architecture, tamper resistance, and mission-critical cryptographic defense.
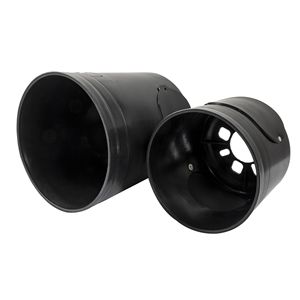
Custom-molded physical intrusion defense chassis with embedded tamper detection sensors designed for critical industrial IoT environments.
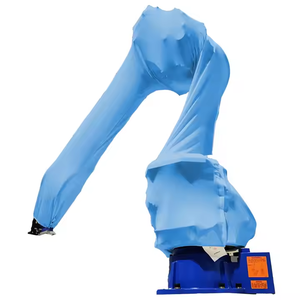
Hardened skeleton protective housing integrated with EMI shielding and active zeroization switches for automated factory robotics.
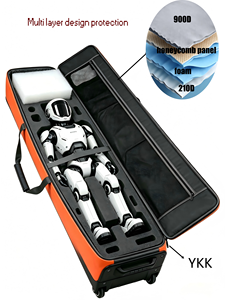
Ruggedized military-grade mobile toolkit box incorporating internal cryptographic key vaults and environmental defense protection.
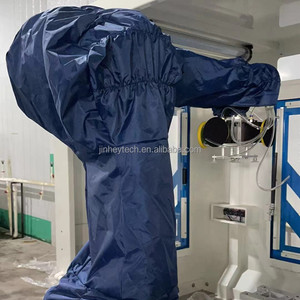
OEM custom thermal management jacket built for secure edge nodes operating in high-heat industrial plant environments.
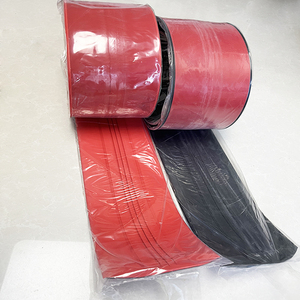
Abrasive-resistant, ultra-durable protection module safeguarding maritime cyber appliances from harsh salt-spray and rock impacts.
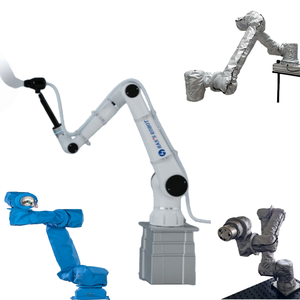
Precision-tailored security suit designed for Universal Robots, KUKA, and ABB arms to prevent physical side-channel tampering.
Washdown-capable protective enclosure specialized for pharmaceutical and food processing cyber-physical hardware infrastructure.
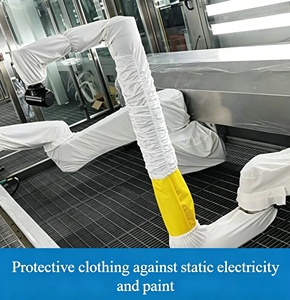
Integrated oilproof, dustproof, and heat-resistant hardware security housing featuring rapid cryptographic zero-wire capabilities.
Combining decades of precision hardware engineering with zero-trust supply chain security for world-class technology vendors.
Our automated manufacturing lines feature secure key-injection chambers. We physically inject cryptographic certificates, Physically Unclonable Functions (PUF), and secure bootloader keys directly into silicon in zero-exposure facilities.
From initial schematic capture and multi-layer PCB design to customized anti-tamper chassis molding, our R&D engineering team translates complex threat models into resilient physical hardware ready for market deployment.
We enforce strict Hardware Bill of Materials (HBOM) traceability. Every resistor, microcontroller, and cryptographic chip is authenticated to prevent counterfeit component insertion and supply chain interdiction risks.
Critical strategic insights for CSOs, Procurement Directors, and Hardware Systems Architects navigating global security compliance.
Enterprise procurement specifications are shifting rapidly toward Quantum-Resistant Silicon. Modern OEM requests require hardware accelerators capable of processing NIST-standardized algorithms (such as CRYSTALS-Dilithium and Kyber). Factories must now support high-performance cryptographic co-processors with updatable microcode to ensure legacy systems remain resilient against quantum decryption vectors.
Passive protection is no longer sufficient for critical infrastructure. Future ODM contracts heavily mandate Active Physical Security. This includes conductive mesh layers, internal light/pressure monitoring, and real-time voltage tamper sensors that instantly trigger physical zeroization—wiping master encryption keys within milliseconds of unauthorized chassis penetration.
Regulatory mandates such as the European Cyber Resilience Act (CRA) require full transparency. Global buyers are choosing OEM partners who provide digitally signed Hardware Bill of Materials (HBOM). Every physical ASIC, firmware build, and driver must carry cryptographic proof of origin, guaranteeing zero unauthorized third-party code or hardware backdoors.
With AI inference moving to industrial edge nodes, physical chips require dedicated hardware execution isolation (Secure Enclaves / TEE). OEMs are increasingly requested to build Heterogeneous Processing Boards that isolate deep learning workloads from administrative management channels, mitigating side-channel attacks on neural network weights.
An Executive Technical Whitepaper on Modern Cyber Security Manufacturing Standards & Silicon Architecture
Historically, enterprise cybersecurity focus was overwhelmingly software-centric, relying on firewalls, endpoint detection and response (EDR), and intrusion prevention software. However, as threat actors increasingly operate at the hypervisor, Unified Extensible Firmware Interface (UEFI), and physical bus levels, software-only security has proven fundamentally insufficient.
Modern industrial and enterprise defense requires a hardware-enforced foundation. OEM/ODM cybersecurity manufacturers now build devices starting at the Hardware Root of Trust (RoT). By embedding an immutable cryptographically secure boot anchor inside immutable Read-Only Memory (ROM), hardware appliances ensure that every layer of software—from stage-0 bootloader to the operating system kernel—is cryptographically verified before execution.
One of the most transformative advances in ODM hardware manufacturing is the integration of Physically Unclonable Functions (PUF). Traditional hardware security relied on storing static cryptographic keys in non-volatile flash memory, leaving them vulnerable to invasive physical extraction techniques such as focused ion beam (FIB) probing or side-channel power analysis.
PUF technology leverages microscopic, naturally occurring random variations inherent in semiconductor manufacturing to generate a unique digital fingerprint for individual silicon chips. The key is never "stored" in static memory; instead, it is dynamically extracted only when needed and vanishes immediately when power is cut. As a leading cyber security ODM factory, embedding PUF silicon into custom IoT gateways and Hardware Security Modules (HSMs) provides an unbeatable physical security posture for enterprise buyers.
Navigating global regulatory landscapes requires OEM/ODM factories to strictly adhere to international manufacturing and engineering benchmarks:
As sophisticated state-sponsored actors and cybercriminals gain access to advanced diagnostic equipment, physical side-channel attacks—such as Differential Power Analysis (DPA), Electromagnetic Analysis (EMA), and Fault Injection Attacks (FIA)—pose severe operational threats to enterprise hardware.
To counteract these vectors, advanced ODM manufacturers incorporate physical countermeasure engineering directly into the PCB layout. This includes deploying multi-layer ground planes to suppress electromagnetic leakage, incorporating noise-generating dummy circuits to obscure power consumption signatures, and embedding micro-sensor arrays that detect localized clock glitching or voltage manipulation, immediately executing a protective hardware shutdown.
Essential answers for engineering teams, procurement leads, and technology partners evaluating OEM/ODM manufacturing capabilities.
We provide complete turnkey customization, including PCB layout redesign, custom chip selection (TPM 2.0, Secure Element, FPGA accelerators), physical anti-tamper enclosure molding, custom metal/plastic color matching, laser-etched branding, customized BIOS/UEFI firmware, and secure key pre-provisioning.
Key injection takes place inside isolated, air-gapped secure rooms certified under ISO 27001 guidelines. Keys are generated via high-entropy hardware random number generators (TRNG) and injected directly into silicon over encrypted channels without human exposure.
Yes. Our engineering and production facilities are equipped to build hardware modules that satisfy FIPS 140-3 Level 3 and 4 requirements, including encapsulated potting compounds, active intrusion detection meshes, and rapid zeroization circuitry.
We execute strict, legally binding Non-Disclosure Agreements (NDAs). All design files, schematics, and microcode are stored on air-gapped internal servers with strict role-based access control (RBAC). Fabrication tasks are compartmentalized so no single department holds complete system blueprints.
Initial engineering samples and rapid-prototype PCBs typically take 3 to 6 weeks depending on schematic complexity. Upon design freeze and tooling approval, mass production lead times generally range between 6 to 10 weeks, inclusive of full functional QA testing.
Yes. While we operate high-capacity SMT lines for high-volume orders, we maintain dedicated flexible production lines to support pilot runs, low-volume high-mix (LVHM) enterprise orders, and specialized defense/industrial hardware projects.
We source 100% of our electronic components directly from authorized tier-1 semiconductor manufacturers or verified global distributors. Every component lot undergoes X-ray inspection and decapsulation testing to verify authenticity before entering SMT assembly.
Our in-house testing facility performs thermal shock testing (-40°C to +85°C), vibration resistance (MIL-STD-810H), ingress protection testing (IP65/IP67/IP68), EMI/EMC compliance screening (FCC/CE), and physical drop impact verification.
Consult directly with our senior hardware security architects. We deliver NDA-protected design evaluations, DFM analysis, and rapid prototyping quotes within 48 hours.
Send an Inquiry
